
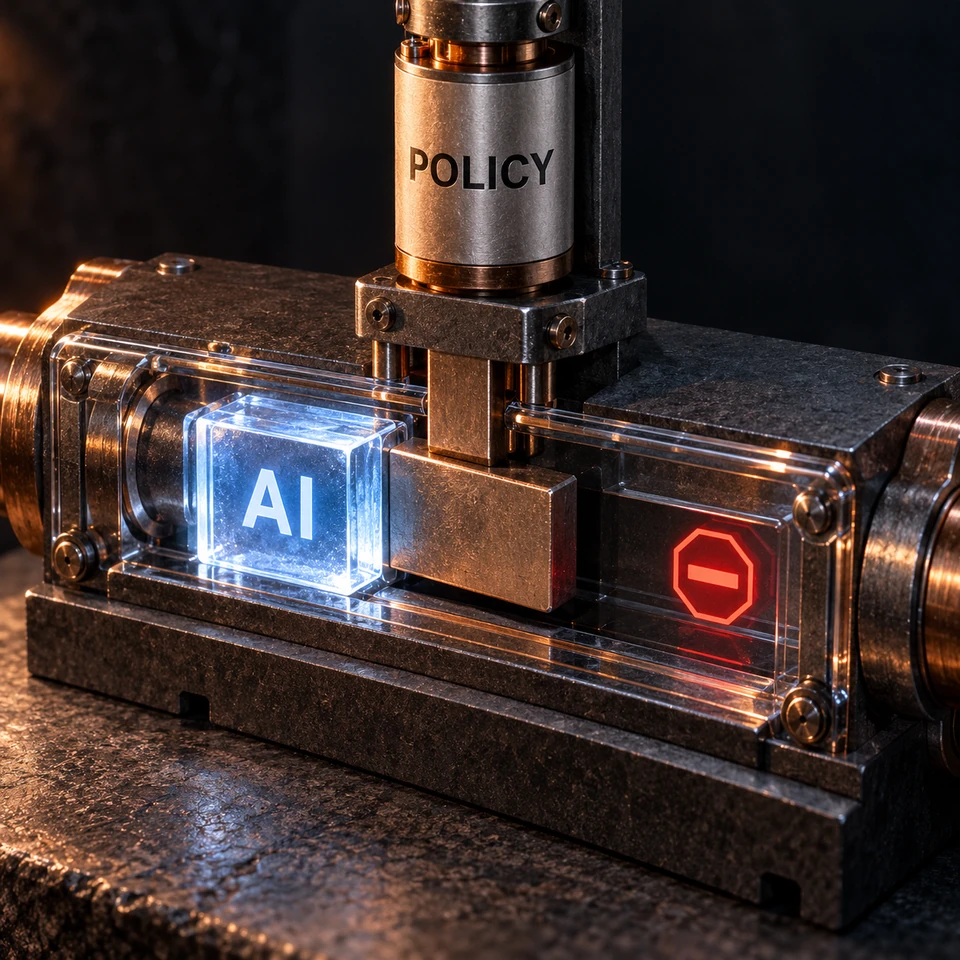
A policy becomes an operational control only when the workflow applies it. Map the consequential actions, define who may permit them and decide where an independent check can stop an action before it executes.
Documentation describes intent
Write the intended rule, its scope, exceptions and accountable owner. Give engineers enough detail to implement it, including what evidence a reviewer needs and what happens when a request is ambiguous.
Gates move the question forward in time
Place the permission check before the consequential write, not only in a later audit report. Test whether direct API calls, retries and alternative tool paths can bypass it, and decide how the process pauses when context is missing.
Policy document vs governance gate: a side-by-side
A policy document defines the intended rule, its scope and accountable owner. A runtime gate checks the proposed action against the implemented rule; an audit record shows the verdict and subsequent outcome. Review tests whether the design and its implementation agree.
Test each part separately: whether the policy is current, whether disallowed actions are blocked, whether missing context pauses the action and whether the recorded verdict matches what executed. A well-written policy or a signed log cannot substitute for that test.
An Operational Control Pattern
For a workflow that sends messages or changes records, pass the proposed action and relevant context to the permission check. Apply the returned verdict, route exceptions to an authorised reviewer and connect the verdict to the execution outcome. This is a design pattern to test, not a reported client deployment.
Why documents still matter
Keep the approved policy and its implementation versioned together. When a rule changes, check the tests, reviewer instructions and evidence format, while retaining the version needed to explain earlier decisions.
The CTO test
Ask which actions can change customer or financial state, where permissions are checked, how exceptions pause work and how an earlier decision can be reconstructed. Start with a bounded workflow, name its owner and test a denied action as well as a permitted one.
FAQ
Do existing human approvals need a new gate platform? Not necessarily. First test their coverage, authority and resistance to bypass. A prompt can guide the model, but consequential tool permissions need a control that does not rely solely on the model following instructions.
EU AI Act: consolidated text, 27 July 2026 | European Commission: AI Omnibus entry into force | GDPR: Regulation (EU) 2016/679